See everything an attacker can — in one platform.
Helios by Isaphia is a unified exposure-management platform. It brings your external footprint, your internal network, threat intelligence, and your cloud posture into a single dashboard — so nothing an attacker could use stays in a blind spot.
Request a DemoYour risk isn't one thing — so one tool was never enough
An attack is a chain: a leaked password, used against an exposed login, to get a foothold, then a quiet walk across an unpatched internal network — and misconfigured cloud along the way.
Point tools show you one link at a time. Helios connects them. External ASM, Internal ASM, CTI, CSPM, and DAST all run against one shared asset inventory, in one dashboard — so you see the whole chain and can break it before it reaches anything that matters.
In plain terms: Helios is a cloud (SaaS) platform you log in to from any web browser. It watches five things at once — what you expose to the internet, what's reachable inside your network, what attackers already know about you, how your cloud is configured, and how your running web apps and APIs behave under attack — and tells you, continuously, what to fix first. You can run it yourself, or have our team operate it for you.
Five modules, one platform
Start with one. Add the rest as you grow. Every module you enable makes the others sharper — because they share the same asset inventory.
External ASM — External Attack Surface Management
Continuously discovers, monitors, and prioritizes every internet-facing asset you own — including the ones you forgot.
- Asset & subdomain discovery
- Vulnerability & TLS monitoring
- Leaked-secret & dark-web exposure
- Email & domain security posture
Internal ASM — Internal Attack Surface Management
Lightweight collectors map what's reachable behind the firewall — the legacy systems attackers pivot to once they're in.
- Internal asset & service discovery
- Legacy-vuln detection (EternalBlue, BlueKeep, SMBv1)
- Automatic CVE correlation
- Multi-site collector coverage
CTI — Cyber Threat Intelligence
Asset-aware threat intelligence. Every indicator is matched against your real inventory — not 50,000 generic IOCs a week.
- Global IOC & KEV feeds
- Leaked-credential & dark-web signals
- MITRE ATT&CK & threat-actor context
- Correlated to your discovered assets
CSPM — Cloud Security Posture Management
Coverage across AWS, Azure, and GCP — misconfigurations, identity risk, and compliance drift, caught early.
- Multi-cloud misconfiguration detection
- IAM & identity risk
- Public-exposure & encryption gaps
- CIS / PCI / SOC 2 / ISO mapping
DAST — Dynamic Application Security Testing
Safely exercises your running web apps and APIs — using black-box and grey-box approaches to surface exploitable flaws like SQLi, XSS, auth bypass, and IDOR.
- Authenticated & unauthenticated web-app testing
- REST & GraphQL API coverage
- OWASP Top 10 & common CWE detection
- Findings correlated to your External ASM inventory
Why one platform beats a stack of point tools
The value isn't five dashboards side by side — it's what happens when they share the same brain.
Every module reads and writes the same living inventory of your assets — external, internal, and cloud. Discover once, use everywhere.
A leaked credential (CTI) against an exposed portal (External ASM) that fronts an unpatched internal host (Internal ASM) reads as one story, not three alerts.
Findings across all five modules are ranked together, so your team works the handful of issues that actually move risk — not five separate backlogs.
SSO, role-based access, and a single pane of glass. No tab-hopping between vendors, no reconciling five exports by hand.
Route everything into Jira, ServiceNow, Splunk, Slack, Teams, or any webhook — from one integration layer, not five.
Turn on modules as you mature. Adding one doesn't mean a new rollout — it lights up inside the platform you already use.
See It in Action
Real screens from the platform — one login, every module. Click any screenshot to enlarge.
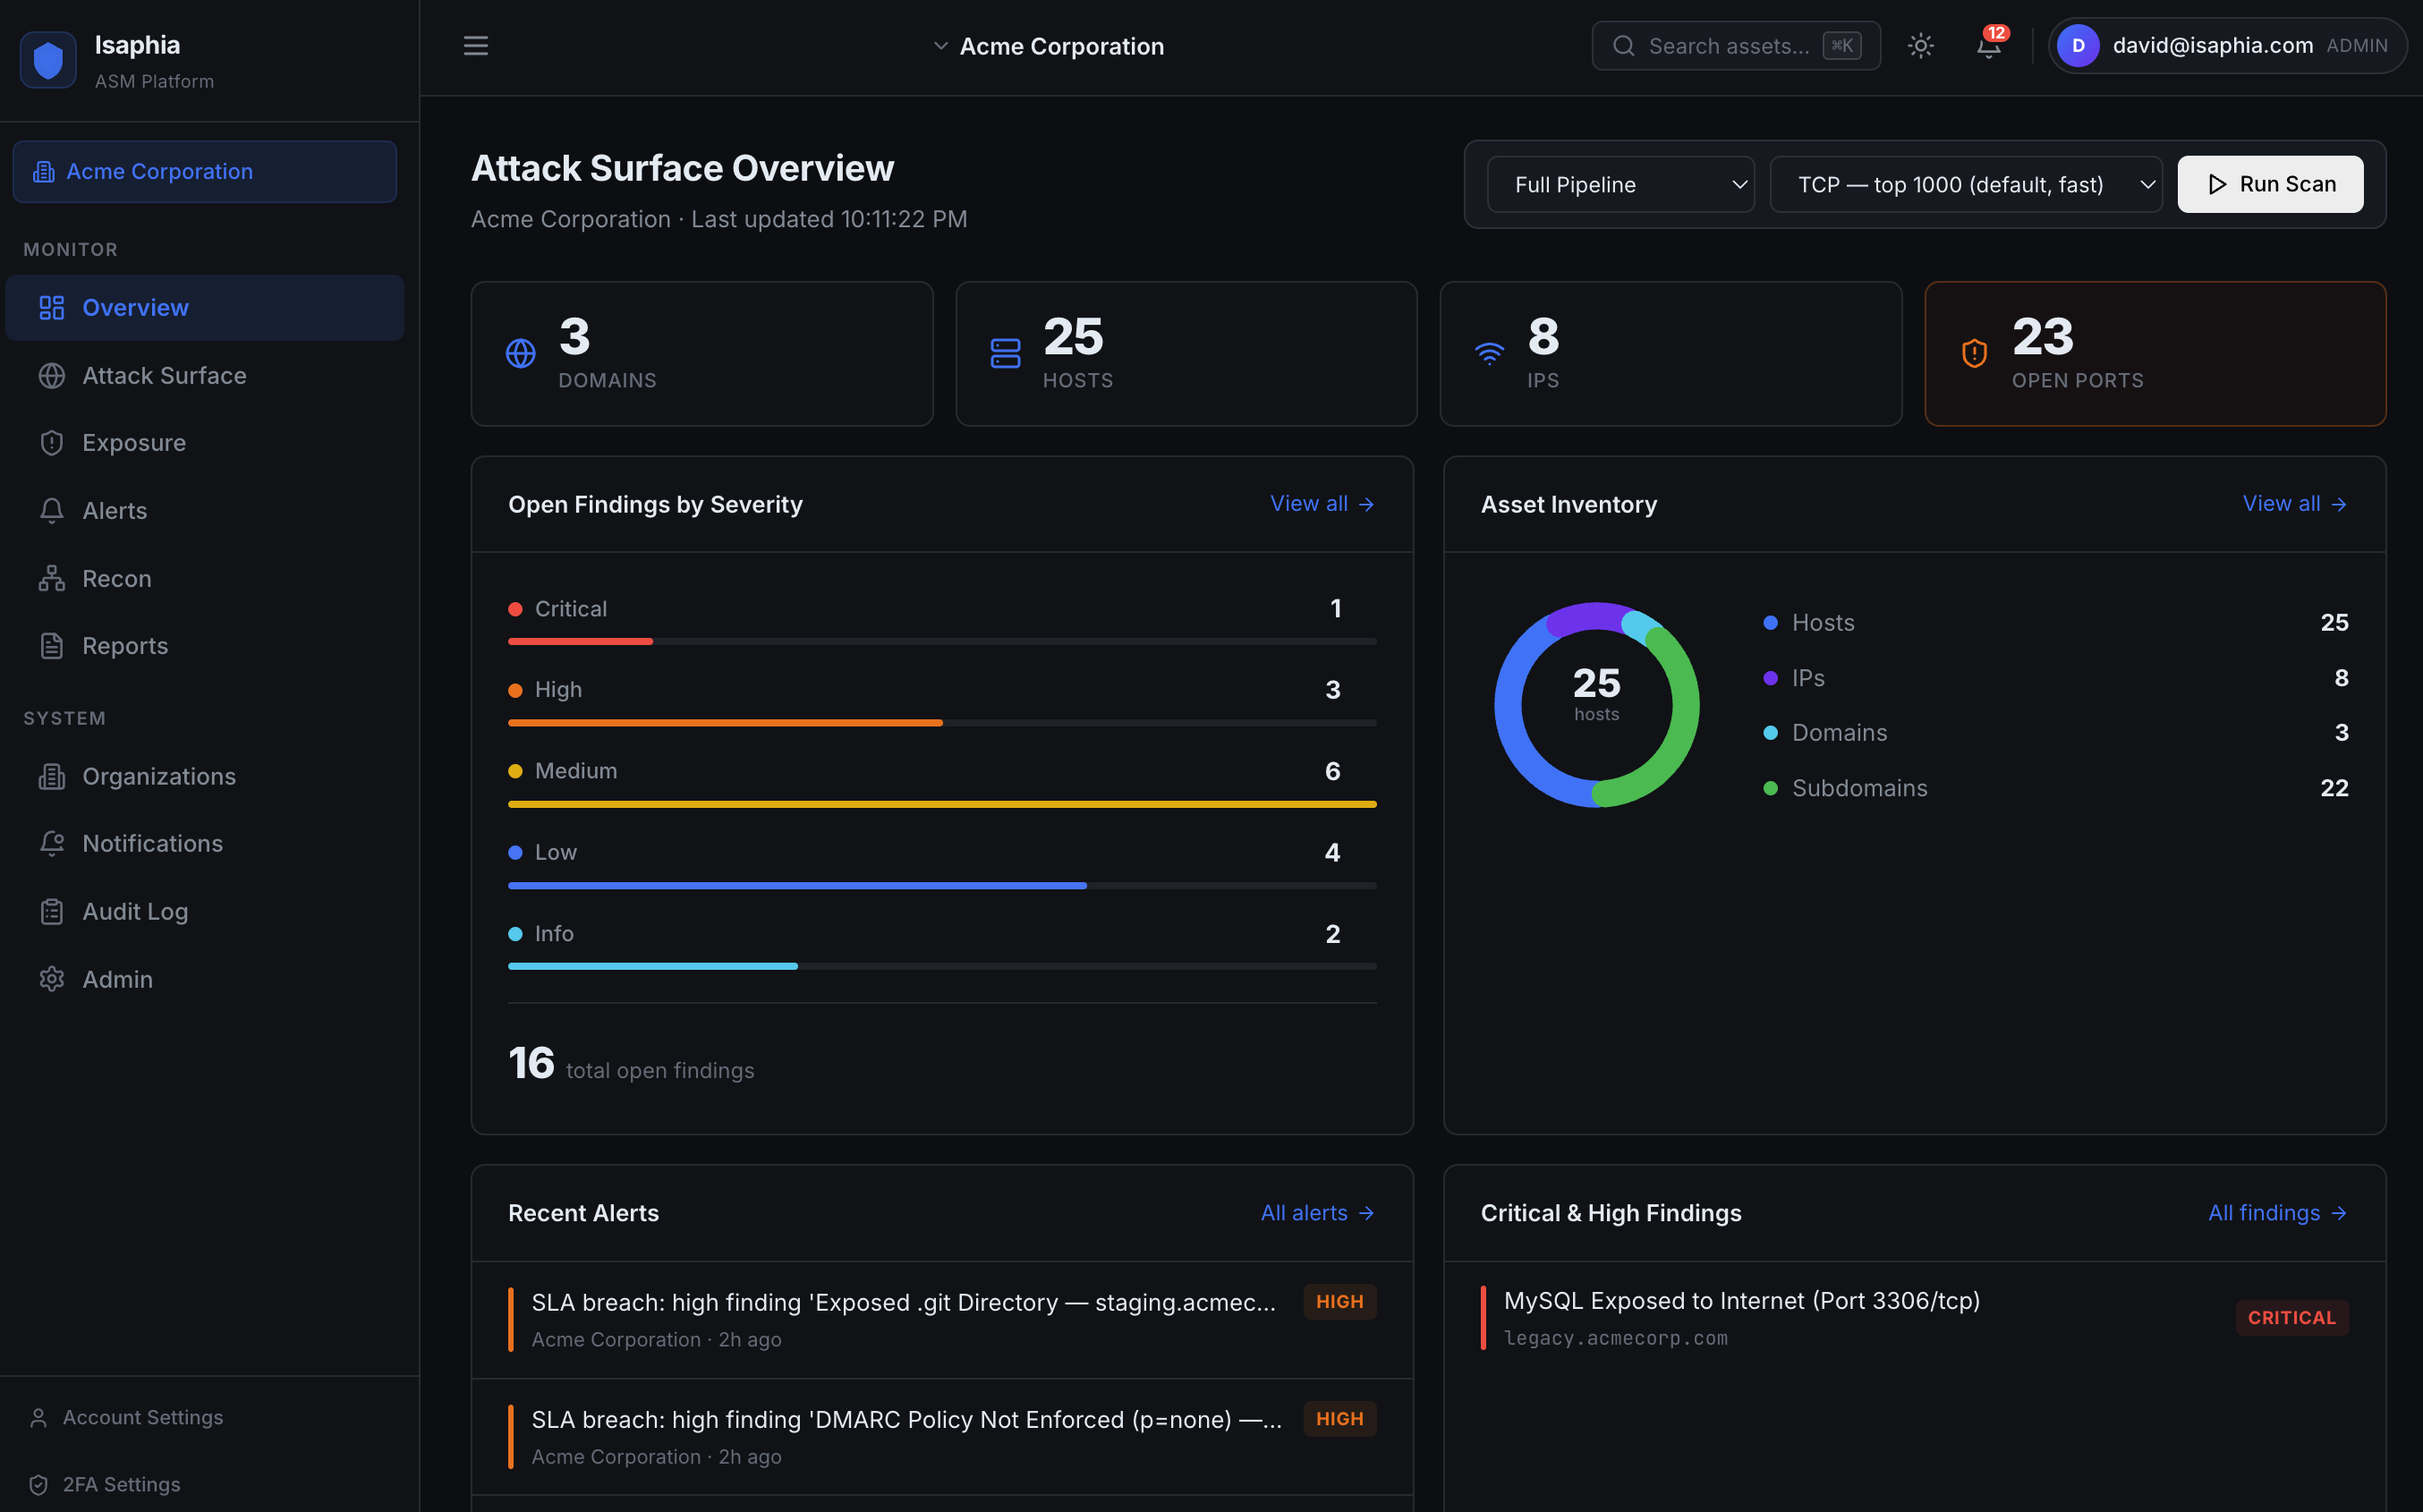
The Helios overview. One security-posture risk score across external assets and cloud, with asset counts, severity breakdown, and the findings that need attention now.
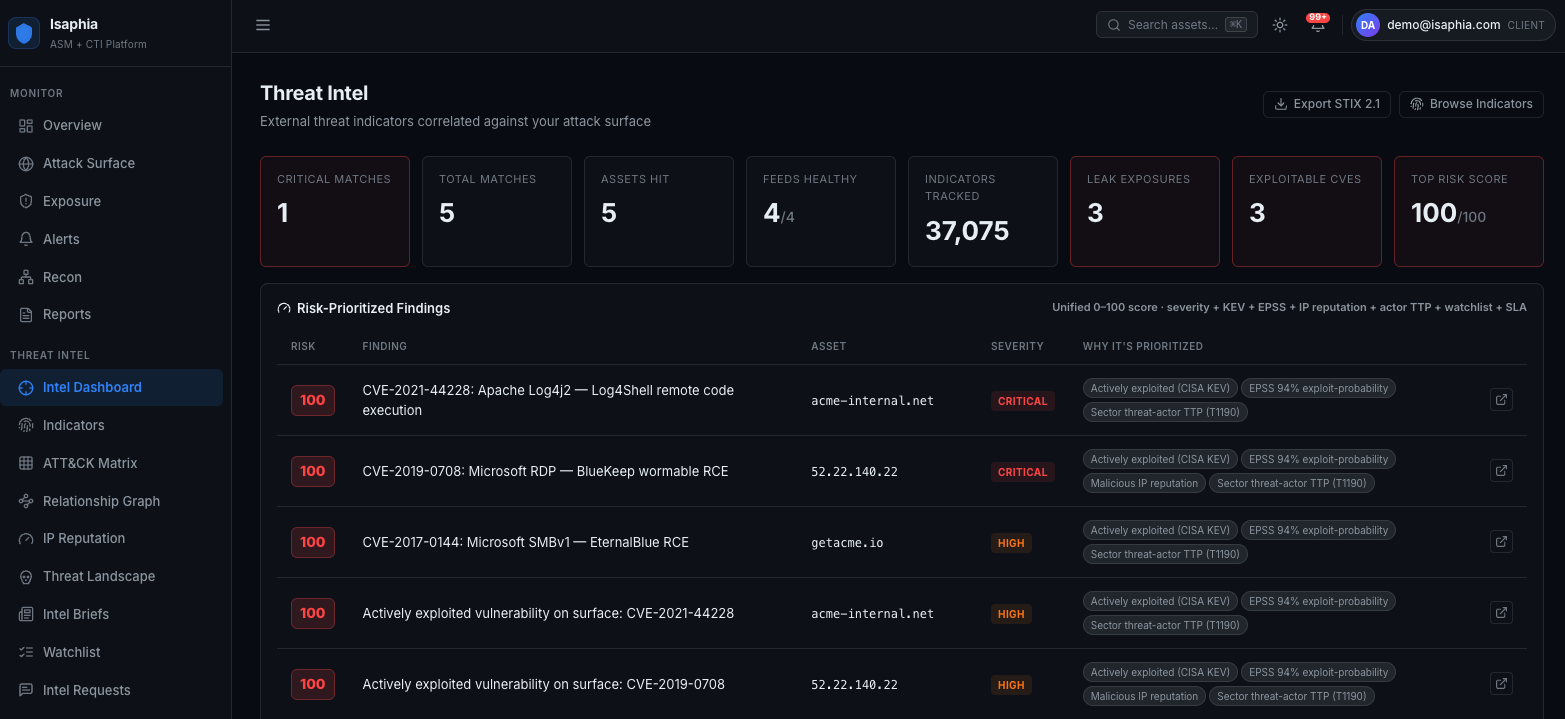
External threat indicators correlated against your attack surface, ranked by one unified 0–100 risk score.
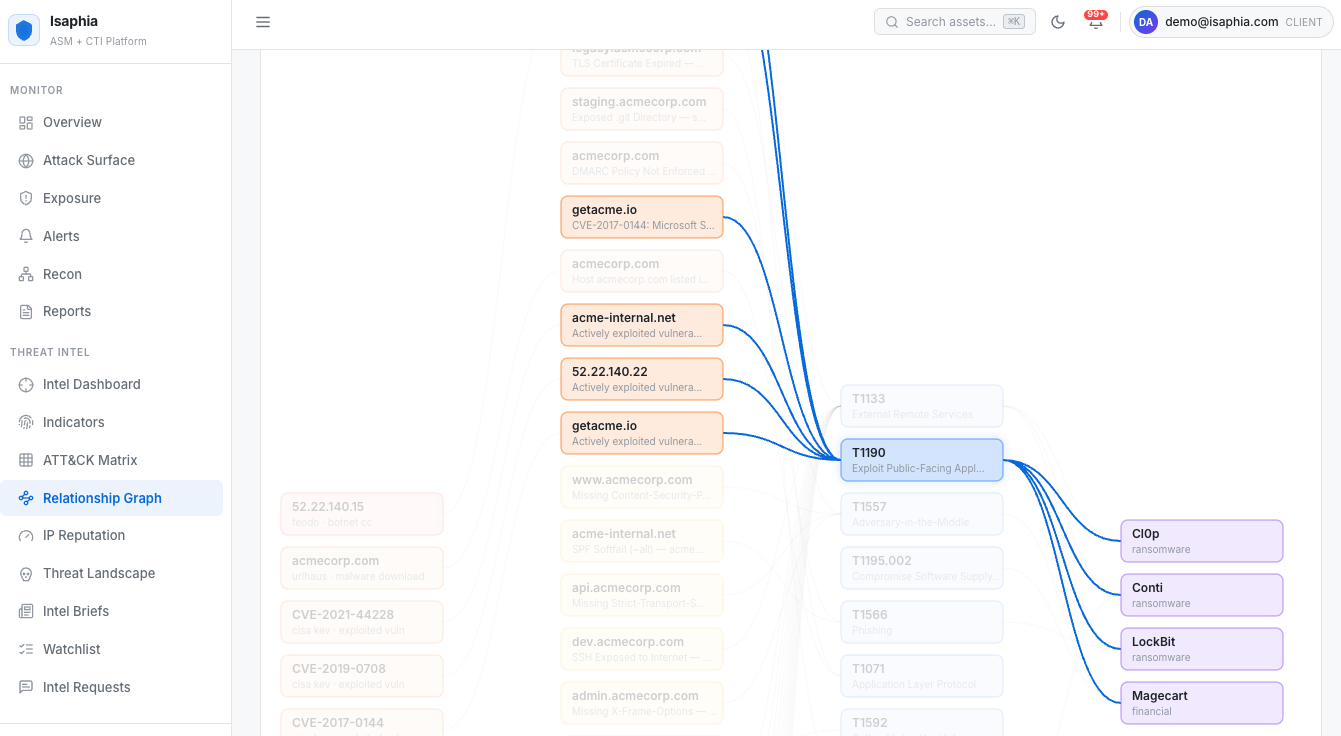
Assets, findings, ATT&CK techniques, and threat actors linked in one relationship graph — the chain, made visible.
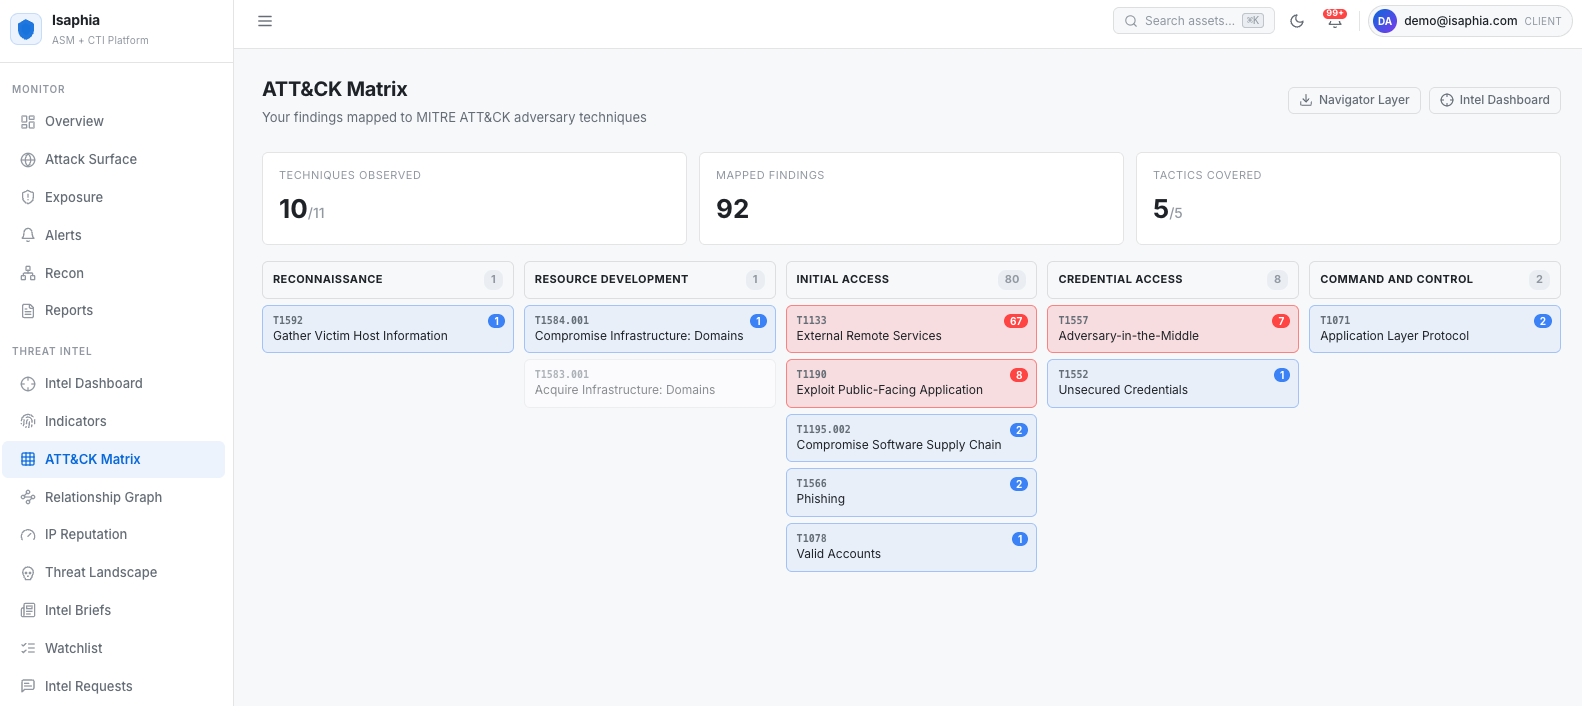
Your findings mapped to MITRE ATT&CK adversary techniques — so you speak the same language as your SOC and your auditors.
One attack. Every angle.
A real intrusion is rarely a single event. It's a chain — and Helios watches every link.
A password shows up in a breach dump. Threat intel flags it against your domain before anyone uses it.
That credential is tried against a login portal you forgot was exposed. External ASM already found — and flagged — that portal.
Inside, they hunt for a flat, unpatched network. Internal ASM has already mapped it and surfaced the EternalBlue box they'd pivot through.
They probe for a wide-open storage bucket or an over-privileged role. CSPM flagged those misconfigurations days ago.
See only one link, and you're guessing about the rest. See every link — in one place — and you break the chain before it reaches anything that matters.
Two Ways to Run It
Same platform, same coverage — choose how much you want to operate yourself.
Run it yourself
Direct dashboard access for your team across every module. Configure scopes, run scans, review findings, export reports. Full RBAC and unlimited users. Ideal for in-house security teams that want hands-on control.
We monitor for you
Our analysts triage findings across all five modules and escalate only what matters. Monthly executive briefings, a direct line to security analysts, and quarterly business reviews. Ideal for organizations without a dedicated cybersecurity team.
Built to Fit Your Stack
Findings from every module go where your team already works — no parallel inbox to babysit.
Frequently Asked Questions
Plain-English answers to the questions we hear most often.
What is Helios by Isaphia, in plain English?
Helios is a single security platform that shows you everything an attacker could use against you: what you expose to the internet (External ASM), what's reachable once someone gets inside your network (Internal ASM), what's already being said, sold, or leaked about you online (CTI), how your cloud accounts are configured (CSPM), and how your running web apps and APIs behave under attack (DAST). It all lives in one dashboard, and you log in from a web browser.
Who is Helios by Isaphia for?
Organizations that have an internet-facing footprint, an internal network, cloud accounts, web apps or APIs, or credentials and data circulating online they can't fully see — and who want all five views in one place rather than five separate tools. That's the whole point of Helios: External ASM, Internal ASM, CTI, CSPM, and DAST against one shared asset inventory. Isaphia's work spans finance, government, retail, hospitality, and nonprofit sectors, in Canada and globally. You do not need a dedicated security team: Helios is built to be readable by an IT lead who wears the security hat part-time, and if you'd rather not watch it day to day, the Managed Service means Isaphia's own practitioners operate it for you.
What modules make up Helios?
Five: External ASM (your internet-facing footprint), Internal ASM (assets and legacy systems inside your network, discovered by lightweight collectors), CTI (asset-aware cyber threat intelligence), CSPM (cloud security posture management across AWS, Azure, and GCP), and DAST (Dynamic Application Security Testing — safely exercising your running web apps and APIs for exploitable flaws).
Do I have to buy all five modules?
No. Most customers start with External ASM and add Internal ASM, CTI, CSPM, and DAST as they mature. The modules share one asset inventory and one dashboard, so each one you add makes the others more useful.
Is Helios a SaaS product?
Yes. Helios is delivered as Software-as-a-Service — you log in from any web browser. You can run it yourself (Self-Service SaaS) or have the Isaphia team operate it for you (Managed Service).
Do I need to install anything?
External ASM, CTI, CSPM, and DAST are agentless — nothing runs on your machines. Internal ASM is the exception: it uses lightweight, safe collectors deployed inside your network to map what's behind the firewall. CSPM connects to your cloud accounts with read-only access, and DAST reaches your web apps and APIs over the network the same way a real user (or attacker) would.
Where is my data hosted?
In Canada by default — across the whole platform, not one module. Findings from External ASM, Internal ASM, CTI, CSPM, and DAST all live in the same managed cloud database, with Canadian data residency in Toronto; EU or US regions are available on request. Isaphia is a Canadian company headquartered in Toronto, operating under PIPEDA and applicable provincial privacy law — which matters if you're subject to Canadian data-residency requirements. Data is encrypted with AES-256 at rest, each customer tenant is isolated at the database query layer, and access is controlled with SAML / OIDC single sign-on, MFA, and an append-only audit log.
How is Helios different from buying separate tools?
Attacks are a chain — a leaked password used against an exposed login to get a foothold, then lateral movement across an unpatched internal network. Separate tools show you one link at a time. Helios correlates all five views against one shared asset inventory, so you see the whole chain and can break it before it reaches anything that matters.
How does pricing work?
Pricing scales with the size of your attack surface and the modules you enable, and whether you choose Self-Service SaaS or the Managed Service. Users are unlimited within your tenant — no per-seat fees. Contact us for a scoped quote.
Built by the people who break in
Helios is built by people who break into networks for a living — the platform we wished we had on engagements.
Isaphia is a Canadian company, headquartered in Toronto, and Helios is built and hosted in Canada — Canadian data residency is the default, not an upgrade. If you're weighing what that means for your obligations, we wrote a guide to attack surface management in Canada, covering PIPEDA, OSFI B-13, and CCCS guidance with links to each regulator. Isaphia's other job is offensive security: penetration tests, red-team engagements, OSINT investigations. Every Helios module started as a question we kept answering by hand for clients — what's exposed to the internet, what's reachable once you're inside, what's already leaked, what's misconfigured in the cloud. We turned that work into a platform, and we still run the engagements that keep it honest.
So when Helios ranks a finding first, it's not a generic severity score — it's the judgment of a team that knows, first-hand, what attackers actually reach for. Meet the team or explore our services.
See your whole exposure — in one place
Get a walkthrough of Helios scoped to your environment. We'll show you what's exposed today, inside and out — and what to fix first.
Talk to Us About Helios